5 Things That Decide Whether a HWID Spoofer Actually Works in 2026
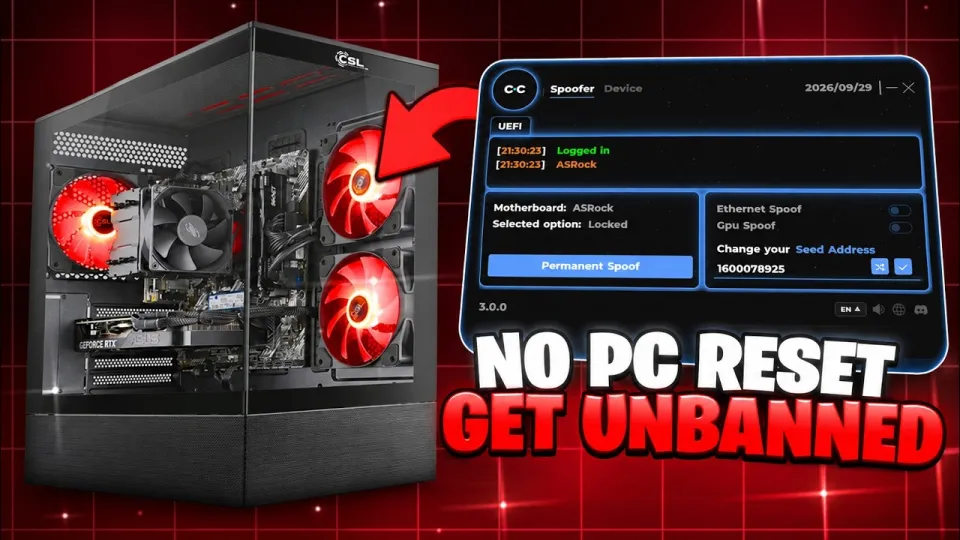
Video: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast
· based on the channel clixx
The best HWID spoofer is the one that replaces every identifier an anti-cheat reads, not just the one you remember being banned on. That means disk and volume serials, SMBIOS and BIOS data, motherboard and GPU identifiers, the network MAC address and the trace files left behind on your drives. The build shown in the clixx tutorial is distributed through the CethCheats store and dashboard, where you can register, check supported games and pick up the current license.
What a HWID spoofer actually changes on your PC
A hardware ID ban is a fingerprint ban: the anti-cheat records a set of machine identifiers at the moment of the ban and refuses new accounts launched from the same fingerprint. A spoofer works by intercepting the calls that read those identifiers and returning substitute values, so the machine presents itself as different hardware.
The identifiers that matter in practice:
- Disk and volume serial numbers, including the serials of every physical drive, not only the system one.
- SMBIOS and BIOS data: system UUID, board serial, chassis serial, BIOS version and vendor strings.
- Motherboard and chipset identifiers, plus the GPU device path and its registry entries.
- Network adapter MAC addresses, both physical and virtual adapters.
- Windows-level traces: registry keys, event logs, prefetch files, recent-file lists and the anti-cheat's own cached files.
A spoofer that touches only the disk serial will pass a superficial check and fail the next one. That is the single most common reason people buy a tool, get back into a game for a day and get flagged again.
The five criteria that separate a good spoofer from a broken one
Judge any hardware ID spoofer against these five points before you pay for it, because the marketing pages rarely mention them.
- Serial coverage. The tool must list which serials it rewrites. If the description only says "HWID changer" without naming disk, SMBIOS, motherboard and MAC, assume the coverage is partial.
- Trace and log cleaning. Permanent bans survive because the anti-cheat reads its own leftover files. A serious spoofer clears trace logs, registry artifacts and cached identifiers as part of the same operation.
- Persistence model. Temporary spoofing resets on reboot, which is fine for testing. A permanent spoof writes the new values so they survive restarts, Windows updates and driver reinstalls.
- Game compatibility list. The tutorial build advertises Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant, plus FiveM servers. Check that the game you actually play is named, and check when the list was last updated.
- Support and updates. Anti-cheat signatures change constantly. A Discord community and a changelog are worth more than a one-time download link, because a spoofer that is not updated stops working quietly.
How the setup process runs in the clixx walkthrough
The tutorial walks through the interface, the configuration panel and the installation in a short sequence, and the structure is typical for this class of tool. You start with an overview of the main window, move to the feature list, open the configuration and settings tab, and then run the installation step that applies the spoof.
What to watch for when you repeat the process yourself:
- Read the configuration tab before clicking anything. It is where you choose between a temporary and a permanent spoof and where the tool shows which components it will touch.
- Close the game and the anti-cheat before applying the spoof. A spoof applied while the anti-cheat is running is often ignored or reverted.
- Reboot after installation. Most spoofers write values that only take effect on the next boot, and skipping the reboot is the second most common cause of a failed spoof.
- Verify the result. Free tools such as serial checkers or a simple `wmic` query in Command Prompt let you confirm that the disk and board serials actually changed.
Spoofing is only half of the unban process
A spoofer changes the machine, but a ban is usually tied to more than the machine. The account itself, the payment method attached to it, the phone number and the network fingerprint all form part of the picture, and a fresh hardware ID on a flagged account gets you banned again within minutes.
A workable sequence looks like this: apply the spoof and reboot, confirm the new serials, create a clean game account, avoid reusing the old email, phone number or payment card, and keep the same network setup only if the spoofer also handled the MAC address. For games with server-side bans such as FiveM, the ban record lives on the server, so a spoofer helps only where the server checks hardware identifiers.
Pricing, licensing and where to get the tool
The spoofer reviewed in the tutorial is sold through the CethCheats store, and the video description carries a discount code, DENYS, for 5% off. Licenses for this category of software typically run from a few dollars for a day pass to a monthly or lifetime key, and the price usually tracks how many components the tool rewrites and how often it is updated.
All links from the breakdown:
- Store and product page: https://cethcheats.cc/
- Community and support: https://discord.gg/ceth
Before buying, confirm three things in the store or on Discord: whether the license is temporary or permanent, whether the game you play is on the current supported list, and whether updates are included for the length of your key. A cheap key that stops working after the next anti-cheat patch is the most expensive option on the market.
Risks, limits and honest expectations
No spoofer is undetectable forever, and any tool that claims otherwise is overselling. Anti-cheat vendors specifically look for spoofing artifacts: mismatched serial formats, identical values across machines, and drivers that hook identifier queries. Kernel-level spoofers carry the added risk of a driver conflict that can leave Windows unbootable, which is why a restore point before installation is not optional.
Spoofing also does not restore a banned account. It gives you a clean machine to start from, and the account, the behavior and the network still have to hold up. Treat the tool as one step in a process rather than a magic button, and expect to redo the process if the vendor pushes a detection update.
Summary
The best HWID spoofer in 2026 is the one with documented serial coverage, trace cleaning, a permanent mode, a current game list and active support, and the build shown in the clixx breakdown ticks those boxes with a store page, a Discord and a 5% DENYS code. Start at the CethCheats store to check the license options and the supported games before you commit, then follow the tutorial's order: configure, close the game, install, reboot, verify. Thanks to clixx for the walkthrough that this breakdown is based on.
Key takeaways
- A working HWID spoofer must change serials for disk, volume, SMBIOS/BIOS, motherboard, GPU and network MAC, not just one identifier.
- The tool covered in the clixx tutorial is distributed through cethcheats.cc with a Discord community and a DENYS coupon code for 5% off.
- Advertised game support in the tutorial build covers Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant.
- Spoofing alone does not lift a ban: the game account, the anti-cheat trace files and the network fingerprint all have to be clean.
- A hardware ID ban is a fingerprint ban, so a spoofer that leaves trace logs or cached identifiers on disk gets flagged again on the next launch.
Questions & answers
Does a HWID spoofer get rid of a game ban?
No. A spoofer changes the hardware identifiers your PC reports, so the machine no longer matches the banned fingerprint. The banned account stays banned, and you need a clean account on the spoofed machine to play again. It also does not help with server-side bans, such as most FiveM bans, which are stored on the server rather than tied to your hardware.
What is the difference between a temporary and a permanent HWID spoofer?
A temporary spoofer changes identifiers only for the current session and reverts them on reboot, which is useful for testing. A permanent spoofer writes the new values so they survive restarts, Windows updates and driver reinstalls. Permanent mode carries more risk if something goes wrong, so create a restore point first.
Which games does the spoofer in the tutorial support?
The description lists Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant, plus FiveM servers. Support lists change as anti-cheats update, so confirm the game you play is still covered on the store page or in the Discord before buying a key.
How much does a HWID spoofer cost?
Prices in this category range from a few dollars for a day pass to monthly and lifetime keys, and the cost usually reflects how many components are rewritten and how frequently the tool is updated. The tutorial includes a discount code, DENYS, for 5% off at the CethCheats store.
Source: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast · Markdown version